
A defense modular data center delivers sovereign capacity in a transportable enclosure — sited at the installation rather than in someone else’s cloud region, and standing up in months rather than a programme cycle.
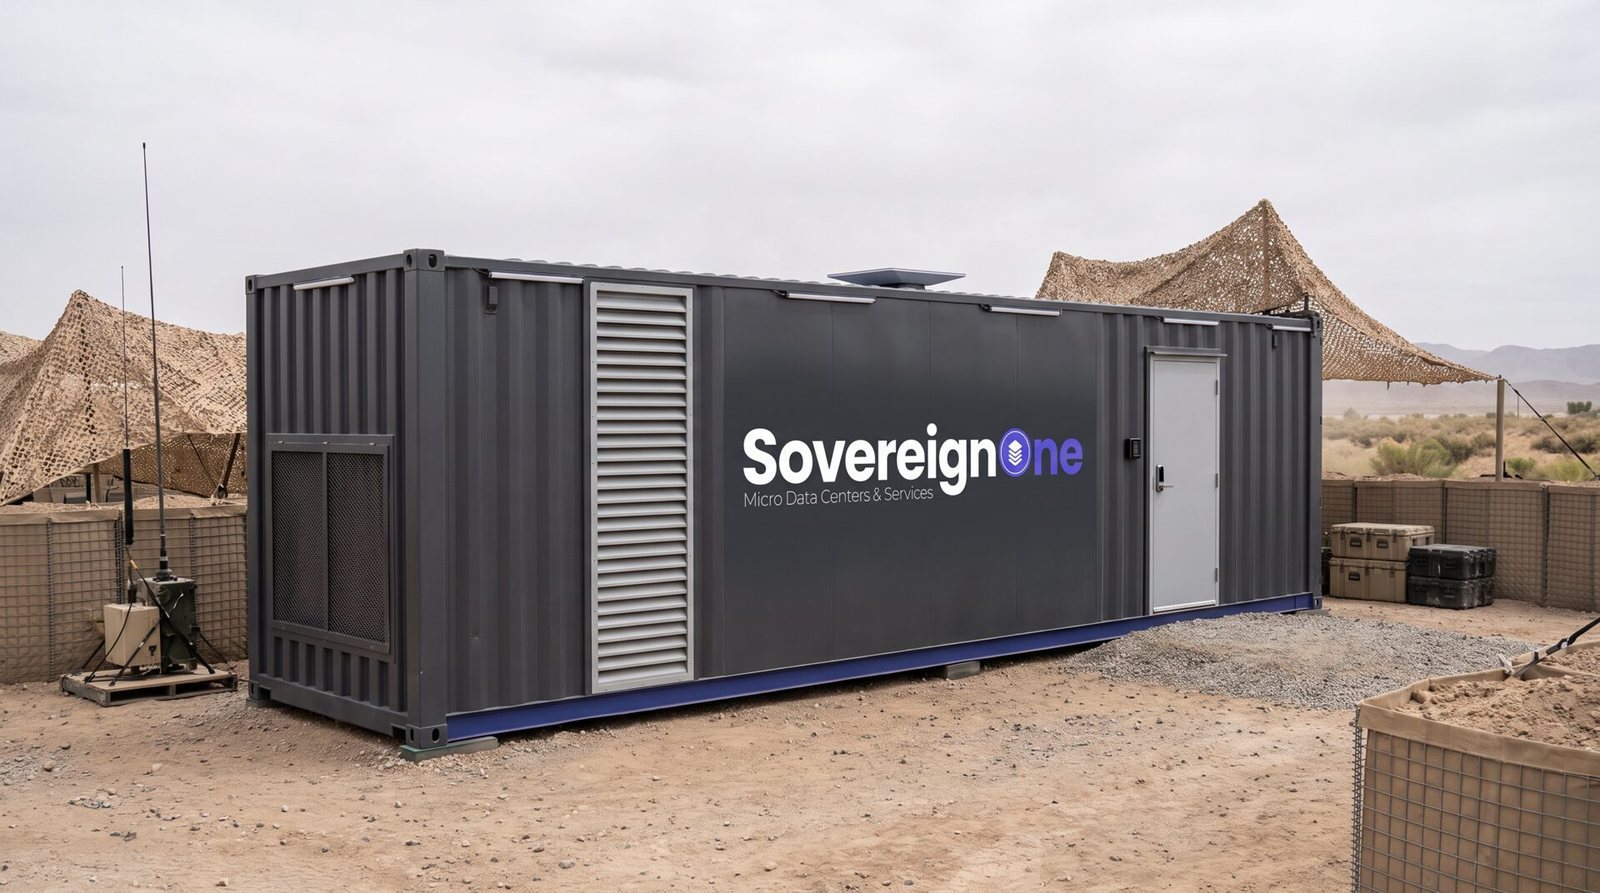
A defense modular data center takes the facility off the critical path. The capability is ready when the unit is energised rather than when a building is finished, and the same unit can be relocated if the mission moves.
Mission compute at the edge of the network, where backhaul is contested or absent.
Added capacity on an existing base without a MILCON programme.
High-density compute near the ranges and simulators that consume it.
Capacity that deploys for an exercise and returns to the motor pool afterwards.
Lengths shown are indicative. The configuration for any site is set during the survey, against the actual load, the power available and the conditions on site.
A defense modular data center puts compute where the mission is, instead of backhauling sensor, ISR and simulation data to a distant region over links that may be contested, congested or simply unavailable. The unit arrives sealed and commissioned, so a site becomes operational without standing up a construction programme behind it.
The five lengths cover a wide range of defense deployments without changing the underlying design: 7 ft with a single rack at a nominal 125 kW, 12 ft with two racks at 250 kW, 20 ft with five racks at 625 kW, 40 ft with ten racks at 1.25 MW, and 52 ft with fourteen racks at 1.75 MW. Every length shares the same cooling, power and security design, so an engineering review completed for one unit holds for the next.
Siting is a question of power and ground rather than construction. A conventional build runs two to five years from permit to energised; a SovereignOne unit runs four to six months from survey to live load, which is the difference between a capability that arrives within a programme cycle and one that arrives after it.
Cooling is where most of the saving sits. The design reduces power and water used for cooling by 30% against a conventional air-cooled hall. On constrained sites, available utility capacity rather than floor space is usually what limits a defense deployment, so that reduction often decides whether a site can host the load at all.
Each unit is integrated from established platforms — CDW, Vertiv, Penguin Solutions, Motivair, Dell, Supermicro, Connected Power, NVIDIA — rather than bespoke hardware. SovereignOne is a Liberation Technology Services company, and Liberation Technology Services Inc. is a WEXMAC prime contract holder.
Operationally the unit behaves like any other facility on the installation. It presents standard power and network interfaces, it is monitored the same way, and spares follow the original vendors’ own support channels rather than a bespoke supply chain. Nothing inside the enclosure is unique to SovereignOne, which is deliberate: it keeps sustainment ordinary.
Where a defense modular data center is used is a programme decision rather than a technical one. The same enclosure supports installation compute, training and simulation, maintenance and logistics analytics, and processing close to sensors — anywhere the data is produced faster than it can reasonably be moved.
A battlefield does not hold still, and the infrastructure supporting it should not be fixed to a building sited for a previous campaign. A mobile modular data center lets compute relocate with the force — set down at an installation, a forward location or a staging area, and moved again when the mission does.
Capability concentrated in one facility is capability that ends with that facility. Spreading compute across several enclosures in several places means the loss of one degrades the picture rather than ending it — which is the posture a contested environment requires rather than a convenience.
Autonomous and semi-autonomous platforms produce and consume data faster than a contested link can carry it. Siting the compute alongside them keeps tasking, sensor fusion and control local, so those systems keep operating when the connection back is congested, jammed or denied.
ISR, sensor and full-motion video are generated far faster than they can be moved. A unit on site becomes the processing hub for its area — turning capture into product where it is collected, and sending conclusions rather than raw feeds back over whatever bandwidth exists.
The same enclosure supports modular command and control facilities and the infrastructure behind sensitive compartmented work: power, cooling, physical security and controlled access built into a unit that can be sited, secured and resited. Accreditation is a program-level process run with the government customer — the unit provides the facility that process is run against.
Yes — that is the point of a container form factor. The unit is set on a pad rather than built into a facility, so the capability is not tied to the site it first deployed to.
Units deploy as multiples, so processing can be distributed across them rather than concentrated in a single building.
The unit provides the compute and the enclosure. Accreditation of the resulting facility is a program-level process run by the accrediting authority — it is not something the hardware carries on arrival.
Because the link back to it is the part most likely to fail. Local processing keeps the capability available when the connection is not.
SOC 2 and ISO 27001 are addressed for each individual deployment rather than carried as a blanket product certification, because the unit sits inside your boundary and the control environment is partly yours. Scope is agreed as part of the deployment.
Send the site, the load and the timeline. We will come back with a length, a power plan and a delivery window.